Threat intelligence helps identify what may pose a threat. Risk intelligence goes further by connecting threats, vulnerabilities, exposure, and consequences to the people, assets, and operations a security team protects, creating a clearer basis for prioritization, protective action, and defensible security decisions.
Threat Intelligence vs Risk Intelligence: What Physical Security Teams Actually Need
Threat intelligence, vulnerabilities, and risk are connected, but they are not interchangeable. For physical security teams, the distinction matters because knowing that a threat exists is only the beginning. The real decision is whether it matters to the people, sites, routes, events, and operations you are responsible for protecting.
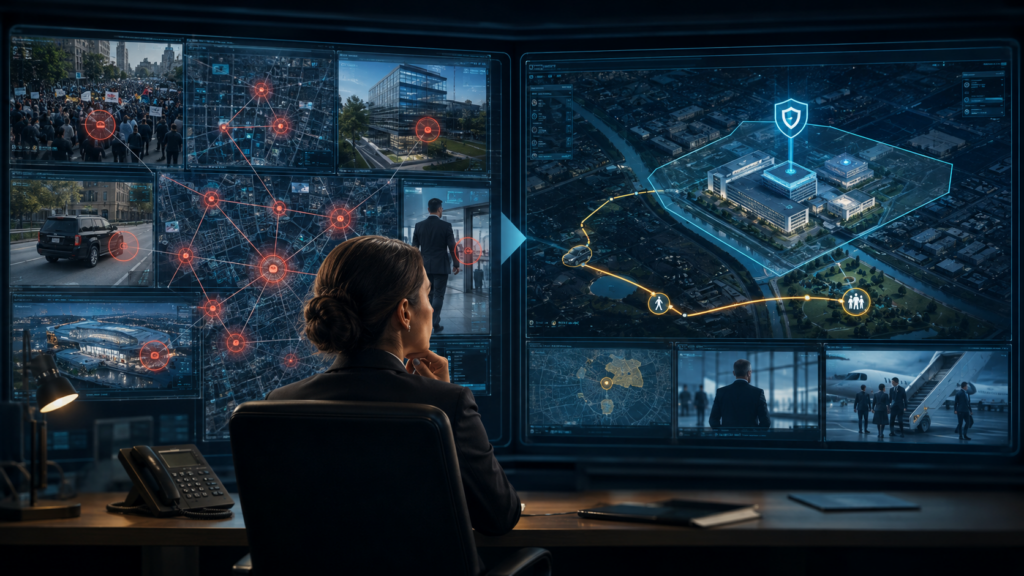
Threat intelligence tells you what is happening, emerging, or capable of causing harm. Risk intelligence connects that threat to a specific asset, vulnerability, exposure, consequence, and decision. Threat intelligence is an input. Risk intelligence is what turns the input into a prioritized security action.
Search for threat intelligence and most of what appears is cyber-focused: threat actors, indicators of compromise, malware, attack infrastructure, and security operations centers. That is a legitimate use of the term, but it is not the whole picture.
Physical security teams also depend on threat intelligence. They monitor civil unrest, crime, targeted violence, geopolitical instability, weather, infrastructure disruption, executive exposure, travel conditions, and emerging incidents that can affect a protective operation. In fact, ASIS International’s 2025 threat intelligence research found that physical security incidents were the threat category respondents rated most highly: 88% said good intelligence on physical security incidents was extremely or highly important.
The question is not whether threat intelligence matters. It clearly does. The question is what happens after the threat is identified.
A security team does not protect “the threat environment” in the abstract. It protects a person, a site, a movement, an event, an organization, or another defined asset. The team has to decide whether a new piece of information changes exposure, whether a vulnerability makes that threat relevant, how severe the potential consequence is, and what should change operationally.
That is where the distinction between threat intelligence vs risk intelligence becomes operationally important.
Why the terminology matters
Security language has consequences. If every negative event is called a “risk,” every weakness is called a “threat,” and every alert is called “intelligence,” teams lose the ability to prioritize. The words start describing everything, which means they stop helping anyone decide anything.
Mature security programs separate the concepts because each plays a different role in the decision process. CISA’s Interagency Security Committee risk-management standard structures physical-security risk around threat, vulnerability, and consequence, while ISO 31000 frames risk around the effect of uncertainty on objectives. The ASIS Security Risk Assessment Standard reflects the same broader principle: security risk should be identified, analyzed, evaluated, and prioritized rather than reduced to a list of threats.
The practical distinction: a threat can exist without creating meaningful risk to your operation. Risk emerges when the threat is connected to something you value, a vulnerability or exposure, a potential consequence, and a realistic likelihood.
What is threat intelligence?
For physical security teams, a useful definition is straightforward: threat intelligence is threat information that has been collected, assessed, analyzed, and put into enough context to support a decision. That is consistent with the definition used in ASIS International’s 2025 threat intelligence research, which distinguishes analyzed and enriched intelligence from raw threat information. A social-media post, police bulletin, weather alert, incident log, or news report is not automatically intelligence simply because it contains information about a threat.
Intelligence requires analysis and context.
In physical security threat intelligence, useful inputs can include:
- civil or political unrest and planned demonstrations;
- local, regional, or organized crime trends;
- workplace violence and concerning behavioral indicators;
- threats or adverse signals involving a principal, executive, family, or organization;
- terrorism, extremism, and targeted violence indicators;
- weather, natural hazards, infrastructure outages, and transportation disruption;
- travel restrictions, geopolitical instability, and destination-specific conditions;
- online exposure, leaked information, impersonation, or digital signals with physical-security implications.
Good threat intelligence is rarely one feed. Useful analysis may draw from open sources, government reporting, trusted partners, incident histories, direct observation, internal reporting, and other relevant sources. The value comes from comparing, verifying, and interpreting those inputs rather than simply collecting more of them.
But threat intelligence still answers a relatively bounded question: What threat conditions exist, and what do we know about them?
What is risk intelligence?
Unlike threat intelligence, risk intelligence does not yet have one universally adopted definition across every security standard. For physical security teams, the useful distinction is functional: risk intelligence connects information to the asset, objective, exposure, consequence, and decision that matter.
A useful working definition for security teams is:
Risk intelligence is assessed information that connects threats, vulnerabilities, exposure, likelihood, consequences, and controls to a specific asset or objective so a decision-maker can prioritize and act.
For the broader framework, including how risk intelligence applies across executive protection, HNW and family office security, corporate security, guard forces, travel, sites and events, and investigations, see our guide to risk intelligence for physical security teams.
That working definition is consistent with broader risk-management thinking. ISO 31000 defines risk around the effect of uncertainty on objectives, while CISA’s physical-security risk guidance treats risk as encompassing threat, vulnerability, and consequence. The common thread is that risk is contextual. It exists in relation to something the organization is trying to protect or achieve.
The terminology is beginning to shift across the wider security profession as well. In April 2026, ASIS International renamed its Operational Intelligence Community the Risk Intelligence Community, describing the change as a better reflection of a broader strategic decision-support mission. That does not define the discipline for Alpha Recon; it is evidence that the wider market is moving toward the same distinction between reporting threats and supporting risk decisions.
That makes security risk intelligence inherently asset-centric. The same protest, individual, weather event, crime trend, or online threat may create very different levels of risk for two different principals, sites, routes, or organizations.
Threat vs risk vs vulnerability: what is the difference?
The phrase threat vs risk vs vulnerability is often treated like a terminology exercise. In practice, it is the foundation of good security prioritization.
CISA’s physical-security guidance provides a useful model: risk is a function of threat, vulnerability, and consequence. Its Interagency Security Committee standard describes vulnerability as a weakness in the design or operation of a facility that an adversary can exploit, with a broader definition that includes physical or operational attributes that make an asset susceptible to disruption or exploitation.
A potential cause of harm: an actor, event, condition, or hazard capable of producing an unwanted outcome.
A weakness or condition that makes a person, site, system, route, or operation susceptible to the threat.
The effect if the unwanted event occurs: harm to people, operations, finances, reputation, mission, or assets.
The potential for an unwanted outcome when threat, vulnerability, likelihood, and consequence are considered together.
This is why a Threat and Vulnerability Assessment is more useful than a list of nearby incidents. The objective is not simply to prove that threats exist. It is to determine which threats interact with actual vulnerabilities and create material exposure that should change the protective plan.
Threat intelligence vs. risk intelligence
Threat intelligence and risk intelligence are not competing disciplines. Good risk intelligence depends on good threat intelligence. The difference is where the analysis stops.
| Question | Threat Intelligence | Risk Intelligence |
|---|---|---|
| Primary question | What is happening, emerging, or capable of causing harm? | What does this mean for the specific person, site, route, event, or objective we protect? |
| Focus | Threat actors, incidents, conditions, hazards, trends, and indicators. | Threat + vulnerability + exposure + consequence + likelihood + existing controls. |
| Typical output | Alert, brief, threat assessment, intelligence update, or situational awareness. | Prioritized risk finding, score, recommendation, mitigation decision, and documented rationale. |
| Unit of analysis | The threat or threat environment. | The protected asset or business/security objective. |
| Operational value | Improves awareness and anticipation. | Supports prioritization, resource allocation, posture changes, and defensible decisions. |
| Relationship | Critical input. | Decision framework that uses threat intelligence as one of several inputs. |
A physical security example: one threat, four different decisions
Consider a common executive-protection scenario. A demonstration is scheduled near a hotel where a principal is staying.
A protest near the principal’s hotel
Threat intelligence confirms the demonstration, expected attendance, organizer intent, timing, location, law-enforcement posture, and recent related activity. That is valuable intelligence, but the protective decision is still incomplete.
A demonstration is planned three blocks from the hotel during the principal’s departure window.
The primary vehicle exit feeds directly into the planned march route, with limited standoff and poor alternate egress.
Movement could be delayed, the principal could be exposed to crowd interaction, and the team could lose route flexibility.
Advance departure, move to alternate egress, stage the vehicle differently, and monitor the route until movement is complete.
Now change one fact. The principal is not at that hotel and has no movement through the affected area. The threat still exists. The intelligence is still accurate. But the risk to that operation may be negligible.
Change another fact. The principal is a high-profile public figure who has recently been targeted by the same activist network. The threat may now deserve a very different rating and protective posture.
This is the difference between situational awareness and decision-grade executive protection risk intelligence. Context changes the risk.
Where physical security threat intelligence often stalls
Security teams are increasingly good at finding information. The harder problem is turning it into a repeatable decision process.
The operational problem is often not access to information. It is the speed and consistency with which a team can verify it, connect it to a protected asset, communicate what matters, and turn it into a decision. A team can be rich in information and still be poor in decision support.
Common failure points include:
- too many alerts with no asset-specific relevance;
- threat information that is not connected to vulnerabilities or existing controls;
- different analysts applying different standards to similar events;
- no consistent method to score or prioritize findings;
- recommendations that disappear into email, PDFs, or chat threads;
- no record of whether mitigation was completed or whether residual risk changed;
- leadership receiving information without a clear decision requirement.
This is why documented risk management matters. The objective is not only to know what changed. It is to preserve the connection between the finding, the decision, the action, and the outcome.
What a strong risk intelligence workflow looks like
A mature security risk intelligence process should move deliberately from information to action. The exact methodology will vary by organization, but the sequence is consistent with established risk-management principles: identify the context, understand threats and vulnerabilities, assess the potential impact, select controls or mitigation, and revisit the risk as conditions change.
Monitor relevant open sources, incident information, trusted partners, direct observations, and internal reporting.
Confirm source quality, corroborate material claims, remove duplicates, and distinguish signal from rumor.
Tie the finding to the specific person, site, route, event, operation, client, or business objective affected.
Evaluate vulnerabilities, exposure, likelihood, consequence, and controls already in place.
Score or rank the risk so resources go to the findings that actually warrant action.
Recommend and implement a control, posture change, route change, staffing adjustment, or other treatment.
Record what was known, what was recommended, what decision was made, and who owns the next action.
Track whether the control held, conditions changed, or residual risk requires another decision.
CISA’s risk-management guidance explicitly treats mitigation and ongoing risk management as part of the process rather than ending the work at identification. The principle is simple: assessment should lead somewhere.
Why risk intelligence matters beyond operations
The value of risk intelligence is easiest to see in the field, but it extends further.
Executive protection and travel
A principal does not need every alert in a destination. The protection team needs the threats and vulnerabilities that could change route selection, hotel choice, timing, staffing, movement, public exposure, or contingency planning. That is why Trip Risk Assessments, Route Recons, Human Risk Assessments, SITREPs, and INTSUMs are more useful when findings are connected to the actual protective decision.
Sites and events
A venue can sit in a generally low-crime area and still contain material vulnerabilities. A high threat environment can also be managed effectively when controls are strong. Threat level alone does not tell a security leader whether staffing, access control, standoff, surveillance, or movement plans are adequate.
Leadership, insurance, and due diligence
A documented risk basis gives leaders something they can review after the immediate operation is over. It can support client briefings, board review, due diligence, counsel, and insurance conversations. Our related guide explains how documented risk intelligence can support lower security company insurance premiums by giving brokers and underwriters stronger evidence of a mature risk process.
Security company risk management
Security firms also carry their own people, leadership, brand, client, digital, and operational exposure. A security company risk management program applies the same discipline internally: identify the exposure, assess what matters, document the decision, and reduce avoidable risk before it becomes a client or liability problem.
Where ARops fits: from threat signal to documented risk decision
ARops is built around the distinction described in this article. It does not treat the alert as the finished product. The objective is to move from scattered signals to verified, asset-specific findings that a security team can act on, explain, and defend.
SecuRecon + Recon Bytes
Continuous monitoring turns relevant signals into analyst-verified updates with context, severity, and relevance tied to protected assets.
Explore the SecuRecon platform →Recon Reports
Finished intelligence products turn verified findings into TVAs, travel and route assessments, human risk assessments, SITREPs, INTSUMs, and other decision-ready reporting.
Explore Recon Reports →ReconOps Hub
Findings, scoring, recommended actions, and mitigation status remain connected so the risk record does not end when a report is delivered.
See documented risk management →The verification layer matters as much as the workflow. Risk decisions become harder to defend when the underlying information cannot be traced or explained. ARops combines AI-assisted monitoring with analyst review and a repeatable verification methodology so the intelligence can be reviewed later, not just consumed in the moment.
The simplest way to think about it: threat intelligence helps identify what may affect you. Risk intelligence determines what it means to what you protect, what should change, and why.
Threat intelligence is not the wrong term. Stopping at threat intelligence is the problem.
Physical security teams absolutely need threat intelligence. They need to identify emerging conditions early, validate information quickly, and understand actors, events, hazards, and trends before they become incidents.
But protective operations ultimately exist to manage risk, not to collect threats.
A threat alert that cannot be connected to an asset is noise. A vulnerability that is not connected to a credible threat may be a lower priority. A risk rating without a recommended action is incomplete. And a recommendation that is never tracked is not a risk-management process.
The shift from threat intelligence to risk intelligence is therefore not a rejection of intelligence tradecraft. It is the next step in making that tradecraft useful to the decision-maker.
The terminology is beginning to shift across the wider security profession as well. ASIS’s 2026 move from “Operational Intelligence” to Risk Intelligence is one visible example of that shift. The more important point is the direction behind it: security is increasingly being asked not simply to report what is happening, but to help organizations decide what matters, what to protect, what to change, and what risk they are prepared to accept.
Frequently asked questions
What is the difference between threat intelligence and risk intelligence?
Threat intelligence analyzes information about threats, actors, events, hazards, and conditions to create useful context. Risk intelligence goes further by connecting that threat information to a specific asset or objective, its vulnerabilities and exposure, the potential consequence, existing controls, and the decision that should follow.
Is threat intelligence the same as a risk assessment?
No. Threat intelligence can be an important input to a risk assessment, but a risk assessment also evaluates vulnerabilities, likelihood, consequences, exposure, and controls. CISA’s physical-security risk methodology treats threat analysis as one part of a broader risk process.
What is the difference between a threat and a vulnerability?
A threat is something capable of causing harm. A vulnerability is a weakness or condition that makes an asset susceptible to that threat. For example, a hostile actor may be the threat; an uncontrolled access point may be the vulnerability that gives the actor an opportunity.
What does risk intelligence mean in physical security?
In physical security, risk intelligence is decision-support intelligence tied to the people, sites, routes, events, operations, and objectives being protected. It combines threat information with vulnerability, exposure, consequence, likelihood, and mitigation context so teams can prioritize protective action.
Why is risk intelligence useful for executive protection?
Executive protection decisions are asset-specific. A general threat may or may not affect a particular principal. Risk intelligence helps determine whether a threat changes the principal’s actual exposure and whether route, timing, staffing, venue, hotel, monitoring, or other protective measures should change.
Move from alerts to decisions you can defend.
See how ARops connects monitoring, analyst verification, Recon Reports, and ongoing risk management for physical security teams.
Schedule a Demo →Sources & Further Reading
- Cybersecurity and Infrastructure Security Agency, The Risk Management Process: An Interagency Security Committee Standard, 2024 Edition
- International Organization for Standardization, ISO 31000:2018 Risk Management — Principles and Guidelines
- Cybersecurity and Infrastructure Security Agency, Chemical Threat and Risk: Threat, Vulnerability, and Consequence
- ASIS International, Threat Intelligence: Understanding How Threat Management Supports Resilient Organizations (2025)
- ASIS International, Risk Intelligence Community: New Name, Focused Mission (2026)
- ASIS International, Security Risk Assessment Standard
Terminology varies by standard, sector, and organization. This article uses CISA/DHS and ISO risk concepts as the primary framework, with ASIS research included as physical-security industry context.